What Is a GRC Program? Essential Elements and How to Build One
A governance, risk, and compliance (GRC) program is an organization’s coordinated approach to setting direction, managing uncertainty, and meeting applicable obligations. It establishes the people, policies, controls, workflows, and reporting needed to connect business objectives with accountable decisions and documented action.
An effective GRC program defines who makes decisions, which risks require attention, what requirements apply, how controls are evaluated, and how issues are resolved. Its scope may include operational, financial, regulatory, cybersecurity, and third-party risks, depending on the organization. This guide explains the essential elements of a GRC program, how to implement them, and how to measure whether the program is working.
Key takeaways (TL;DR)
- Understand the core elements of Governance, Risk, and Compliance (GRC).
- Learn how strong governance drives accountability, transparency, and ethical practices.
- Discover why risk management integration is vital for safeguarding organizational objectives.
- Explore how compliance management streamlines regulations, policies, and internal controls.
- See how GRC breaks down silos and boosts cross-functional collaboration.
Think of GRC as a glue that holds together your business goals and helps you ensure that you comply with your company’s policies and regulations and reduce the risks associated with them. Since GRC offers a structured and scalable framework for managing compliance, governance and security, it makes it the go-to place for all your information security management needs.
This article discusses the elements of a successful GRC governance program, its obstacles, and how to create one that aligns with the needs of all departments within an organization.
About governance risk and compliance (GRC)
According to the Open Compliance and Ethics Group (OCEG), GRC is an integrated collection of capabilities that facilitate the achievement of objectives reliably, address uncertainty, and ensure that ethical behavior is always adhered to by the organization.
What Is GRC?
GRC stands for Governance, Risk, and Compliance. It is an integrated approach that helps an organization set direction, manage risks, and meet its obligations. GRC connects business decisions with clear responsibilities, policies, controls, and oversight.
What Is a GRC Program?
A GRC program puts governance, risk management, and compliance into practice through defined roles, processes, policies, controls, and reporting. It establishes how an organization identifies risks, assigns responsibilities, monitors requirements, evaluates performance, and resolves issues.
The Three Elements of GRC
| Element | What it means | Key activities | Example |
|---|---|---|---|
| Governance | How an organization sets direction, makes decisions, and holds people accountable | Establishing objectives, defining decision authority, approving policies, assigning responsibilities, and reviewing performance | Leadership approves an information security policy, assigns an accountable owner, and reviews implementation progress |
| Risk Management | How an organization identifies and addresses uncertainty that could affect its objectives | Identifying risks, assessing likelihood and impact, selecting responses, implementing controls, and monitoring exposure | A team assesses the risk of unauthorized access and introduces access reviews and approval controls |
| Compliance | How an organization meets applicable legal, regulatory, contractual, and internal requirements | Determining applicable obligations, maintaining policies, assigning compliance activities, collecting evidence, and addressing gaps | A manager completes a required access review, documents the results, and tracks any necessary corrections |
The three elements work together: governance establishes direction and accountability, risk management determines what needs attention, and compliance supports adherence to applicable requirements. A GRC program connects them through consistent processes and documented follow-through.
What Does a GRC Program Need to Operate Effectively?
Governance, risk management, and compliance are the three core elements of GRC. Putting them into practice requires clear accountability, reliable information, and repeatable processes. The following checklist helps organizations assess whether those foundations are in place.
| Program requirement | What should be in place | Practical deliverable |
|---|---|---|
| Program direction | Agreed objectives, organizational boundaries, and executive support | Approved program charter |
| Accountability and oversight | Defined decision authority, responsibilities, and escalation routes | Responsibility matrix and reporting structure |
| Risk management approach | Consistent criteria for assessing risks, selecting responses, and accepting residual exposure | Risk assessment methodology and risk register |
| Obligations inventory | Documented requirements with applicability, ownership, and review dates | Maintained obligations register |
| Policies and controls | Approved guidance and controls connected to relevant risks and requirements | Policy library and control inventory |
| Employee guidance | Accessible instructions and training appropriate to each role | Communication materials and training records |
| Evidence and assurance | Standards for supporting records, control testing, and independent review where appropriate | Evidence requirements and assurance schedule |
| Issue resolution and reporting | Processes for tracking gaps, validating closure, and informing leadership | Corrective-action register and management reports |
How to Build a GRC Program: Seven Practical Steps
Build the program in manageable stages. Begin by understanding existing practices, then test a defined scope before expanding across the organization.
| Step | Implementation action | Completion checkpoint |
|---|---|---|
| 1. Agree on the initial scope | Select the business objectives, entities, processes, and requirements the first phase will cover. Secure sponsorship and resources. | Leadership approves the scope, sponsor, and implementation responsibilities |
| 2. Review existing practices | Gather current policies, risk assessments, control records, audit findings, and reporting processes. Identify what can be retained and where gaps exist. | A documented baseline distinguishes working practices from missing capabilities |
| 3. Set implementation priorities | Rank gaps using risk exposure, mandatory deadlines, business impact, and dependencies. | Each priority has an agreed action, owner, and target date |
| 4. Design and document workflows | Define how teams will assess risks, complete activities, submit evidence, review exceptions, and escalate issues. | Participants understand their responsibilities and handoffs |
| 5. Prepare systems and users | Organize records, configure the chosen tools, establish access permissions, and train participating employees. | Users can complete their assigned work and retrieve the required information |
| 6. Run a pilot cycle | Test the workflows in one department, location, or compliance program. Include evidence review and an overdue or exception scenario. | The team resolves pilot issues and confirms readiness to expand |
| 7. Expand and review performance | Roll out the validated approach in phases. Review adoption, overdue activities, evidence quality, and unresolved findings. | Management uses results to approve improvements and the next rollout phase |
Who Owns a GRC Program?
A GRC program typically has an executive sponsor who provides authority and resources, supported by a designated leader who coordinates implementation and reporting. Business and functional owners remain responsible for managing their risks, operating controls, and completing compliance activities. Legal, compliance, risk, IT, and other specialists provide guidance within their areas, while internal audit provides independent assurance where applicable. Documenting these responsibilities helps prevent gaps between central oversight and everyday execution.
GRC Program Example: Managing Multiple Locations
A company operating across several locations requires quarterly reviews of access to sensitive business systems. Its GRC program connects this requirement with local responsibilities, supporting evidence, management oversight, and corrective action.
Assign the activity. The central team documents the requirement, identifies the systems and locations in scope, and establishes a review schedule. Each location receives an assigned owner, deadline, and evidence checklist.
Collect supporting evidence. Local owners review user accounts with the appropriate managers. They submit records showing which accounts were checked, what access was approved, and which changes were requested.
Review the results. A designated reviewer checks whether the submission covers the required systems and documents the decisions made. Incomplete records return to the owner for clarification.
Address exceptions. If the review identifies an account belonging to a former employee, the team assigns a corrective action to remove access. Closure requires confirmation that the change was completed.
Report to management. Leadership receives a consolidated view of completed reviews, missing evidence, overdue activities, and unresolved exceptions. Repeated issues at several locations may prompt changes to the employee offboarding process.
Governance establishes accountability and oversight, risk management informs the safeguards, and compliance activities document whether the requirement has been met.
How to Measure GRC Program Effectiveness
Measure whether responsibilities are being fulfilled, evidence supports completed work, and identified weaknesses are being resolved. Use consistent definitions and reporting periods so results can be compared meaningfully.
| Metric | How to measure it | What it reveals |
|---|---|---|
| Ownership coverage | In-scope obligations with an accountable owner divided by total in-scope obligations | Whether requirements have clear responsibility |
| On-time completion | Activities completed by their deadlines divided by all activities due during the period | Whether teams execute required work reliably |
| Evidence quality | Submissions accepted on first review divided by total submissions reviewed | Whether records meet established review criteria |
| Overdue corrective actions | Number, age, and priority of actions remaining open past their deadlines | Where unresolved weaknesses need escalation |
| Repeat findings | Findings that recur after an earlier issue was reported as resolved | Whether corrective actions address underlying causes |
Interpret these measures together. High completion rates offer limited reassurance if supporting evidence is incomplete. Similarly, closing many corrective actions means little if the same findings continue to recur.
Break results down by department, location, or program to identify patterns that organization-wide averages may conceal. Review high-priority exceptions individually and investigate changes in performance before drawing conclusions.
Set targets using the organization’s obligations, risk exposure, and baseline performance. Management reviews should turn the results into decisions about resources, controls, training, and follow-up.
Common GRC Program Challenges and How to Address Them
GRC programs often struggle when agreed processes are difficult to carry out consistently. Addressing these operational barriers helps teams turn policies and plans into reliable execution.
| Challenge | Practical response |
|---|---|
| Unclear ownership | Assign one accountable owner to each risk, obligation, control, and corrective action. Document supporting roles and escalation routes. |
| Inconsistent assessments | Establish shared scoring criteria, examples, and reviewer guidance. Periodically compare assessments across teams to identify differences in interpretation. |
| Disconnected records | Connect requirements with relevant policies, controls, activities, and evidence. Define where approved records are maintained and how updates are managed. |
| Excessive implementation scope | Begin with a defined business unit or priority program. Validate the approach before adding more locations, requirements, or workflows. |
| Weak follow-through | Give corrective actions owners, deadlines, and closure criteria. Require supporting evidence and review before marking significant issues resolved. |
Review these challenges during the pilot and after rollout. Recurring late submissions, rejected evidence, or reopened findings can indicate that a workflow needs clearer instructions, better resourcing, or simpler handoffs.
How VComply Supports GRC Program Management
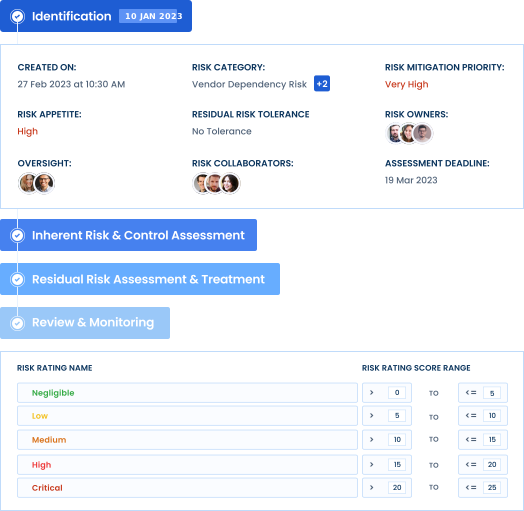
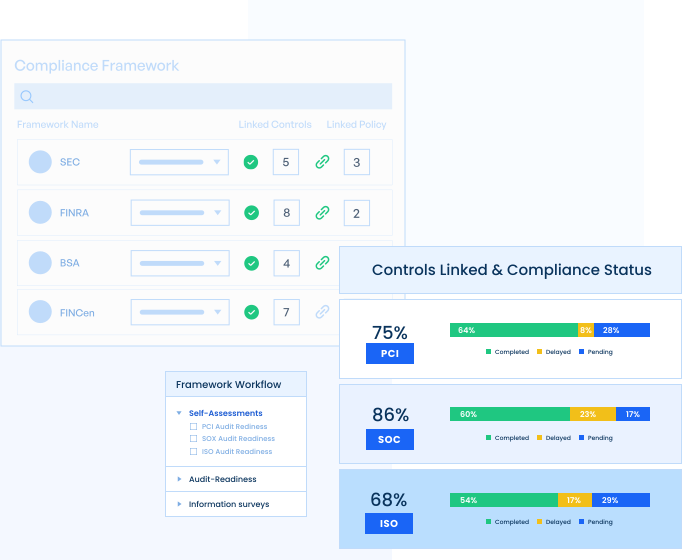
VComply helps organizations coordinate compliance responsibilities, policies, risks, and supporting records through connected workflows. Teams can assign activities, establish deadlines, collect evidence, and monitor progress while maintaining visibility into outstanding work.
ComplianceOps supports recurring compliance responsibilities, reminders, escalations, and performance reporting. PolicyOps helps teams manage policy reviews, approvals, distribution, and employee acknowledgments. RiskOps supports structured risk assessments and tracking of risk responses. Organizations can select the capabilities that match their program’s scope.
For teams working across departments or locations, these workflows help connect central oversight with local accountability. Managers can review progress, follow up on overdue activities, and locate records supporting completed work.
A useful evaluation starts with a real process your team already manages. Request a VComply demonstration using one recurring obligation, its assigned owner, evidence requirements, review steps, and reporting needs. This helps you assess how the platform would support your organization’s everyday GRC activities.
Discover what makes VComply a top G2 high performer in the GRC platform category. Book your demo now and explore its robust capabilities.
Frequently Asked Questions
Can a small organization implement a GRC program?
Yes. Start with priority risks, applicable obligations, named owners, and simple review processes. Expand the program as operations and requirements grow.
Does a GRC program require dedicated software?
No. A small program can begin with controlled documents and registers. Dedicated software becomes useful when coordination, recurring activities, evidence volumes, or reporting needs become difficult to manage.
When should a GRC program be reviewed?
Use a defined review schedule and reassess after significant changes, such as new regulations, acquisitions, incidents, major audit findings, or changes to business operations.